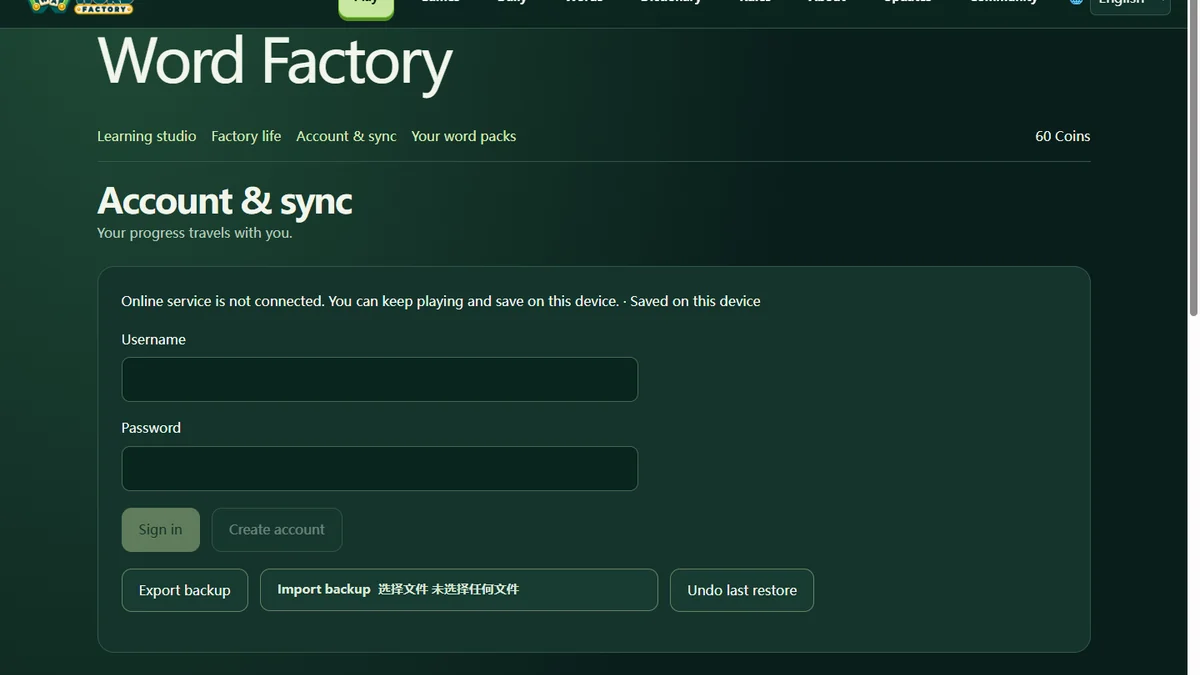
This release focuses on account and publishing controls rather than visible gameplay. It separates ordinary player actions from sensitive administration, adds recovery safeguards and requires reviewed educational content to pass explicit workflow states before publication.
The features described here are part of the production-oriented application layer. External email delivery and public account features remain dependent on approved provider and server configuration; the existence of an interface does not mean every service is enabled publicly.
Account recovery and sessions
Email verification and password recovery use single-use links with short expiry windows. Recovery requests return a neutral response so that the form does not disclose whether an address belongs to an account. A successful password reset revokes existing sessions, reducing the chance that an older session remains active after credentials change.
A retryable notification outbox separates the creation of an email task from delivery. This allows failed delivery attempts to be handled without pretending that a message was sent. External delivery stays disabled until a real provider and sender configuration are available.
Administrator protection
Administrator access requires a time-based one-time password authenticator. Authenticator secrets are encrypted outside the database, sensitive sessions have a shorter lifetime, one-time recovery codes are supported and replayed authenticator codes are rejected.
These controls reduce common account risks but do not eliminate the need for protected devices, strong primary credentials, careful recovery-code storage and server monitoring. Recovery codes should be stored away from the browser session they protect.
Learning-content review
Translations, teaching pages and vocabulary releases move through draft, reviewed and published states. The author cannot review their own draft, and the reviewer cannot perform the final publish action. Vocabulary packs use the same separation so that a general content endpoint cannot bypass the release gate.
The purpose is accountability: a public word, translation or teaching claim should have a visible path from creation to review. The workflow does not itself prove that every claim is correct, so source checks and educational review remain required.
Verification performed
The account-security lifecycle passed 15 isolated staging checks, and the editorial approval workflow passed 13. Browser smoke checks were completed in Chrome, Edge and Firefox without reported runtime errors for the tested flows. Those checks cover the stated build and do not replace production monitoring or an independent security assessment.
Current limitations
Public posting, mail delivery and account synchronization should remain disabled when their production database, moderation, child-safety or provider requirements are incomplete. Players can continue to use guest gameplay without creating an account. For current data handling, see the Privacy Policy; for corrections to this record, use the contact page.